Red · Security
Give your analysts the full investigation behind every alert.
Red brings logs and events from across your estate into one investigation, so analysts triage faster, follow cases through and report with evidence.
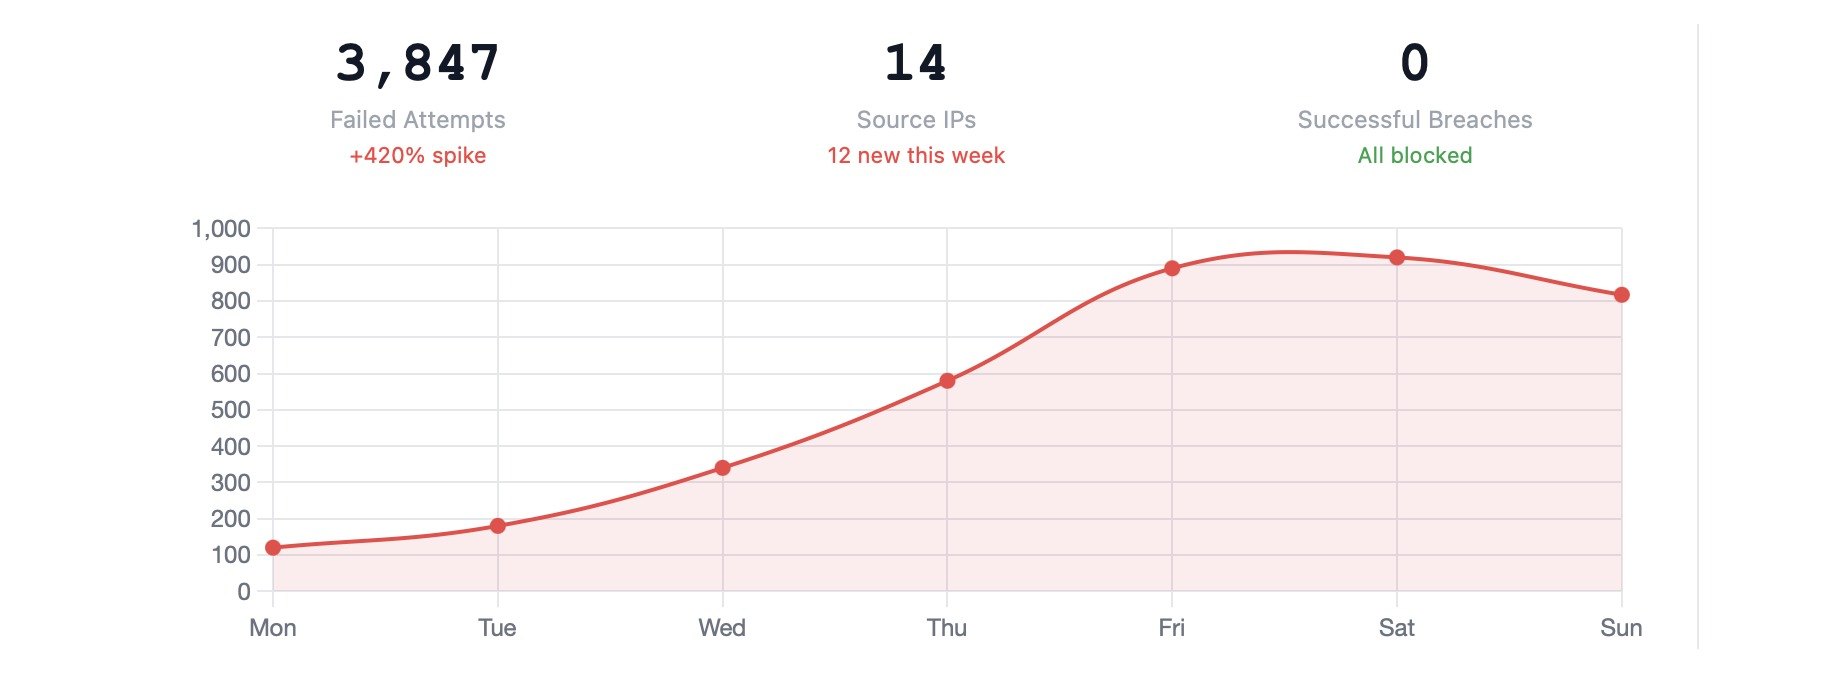
Product screen shown with illustrative demo data.
Decisions it improves
- Which alerts deserve attention first
- What happened, and across which systems
- What to report, and to whom
Questions your team can ask
- “Which of today’s alerts are linked?”
- “What did this account do across our firewall and endpoints?”
- “What evidence supports this case report?”
Built for
Security teams and IT leaders running multi-vendor environments. Pair Red with Megin SecureIt for staffed monitoring and response.
What you can measure
Triage time per case, and how often your analysts agree with the findings.
Connects to
Logs in csv, txt, xml, .log, json, evtx and more. Tested with SentinelOne, Fortinet and other security vendors.
Your environment, your data
Megin Insights runs in your cloud tenant or on-premises. Saga, our orchestration AI, does the heavy lifting inside your environment, and only anonymised, partial information reaches an external model. Saga declines out-of-scope questions locally, and records only that a decline occurred.
Prove before Use
You see Security working on your own data before you commit to a fee.
Agree the measures
Before go-live, we agree up to three success measures with you, each with a baseline from your own data.
Use it for 90 days
Megin Insights runs live in your environment from day one. The 90-day evaluation is fee-free.
Decide on the evidence
Measures met: the annual fee spreads over the remaining nine months. Measures missed: you walk away and owe nothing.